
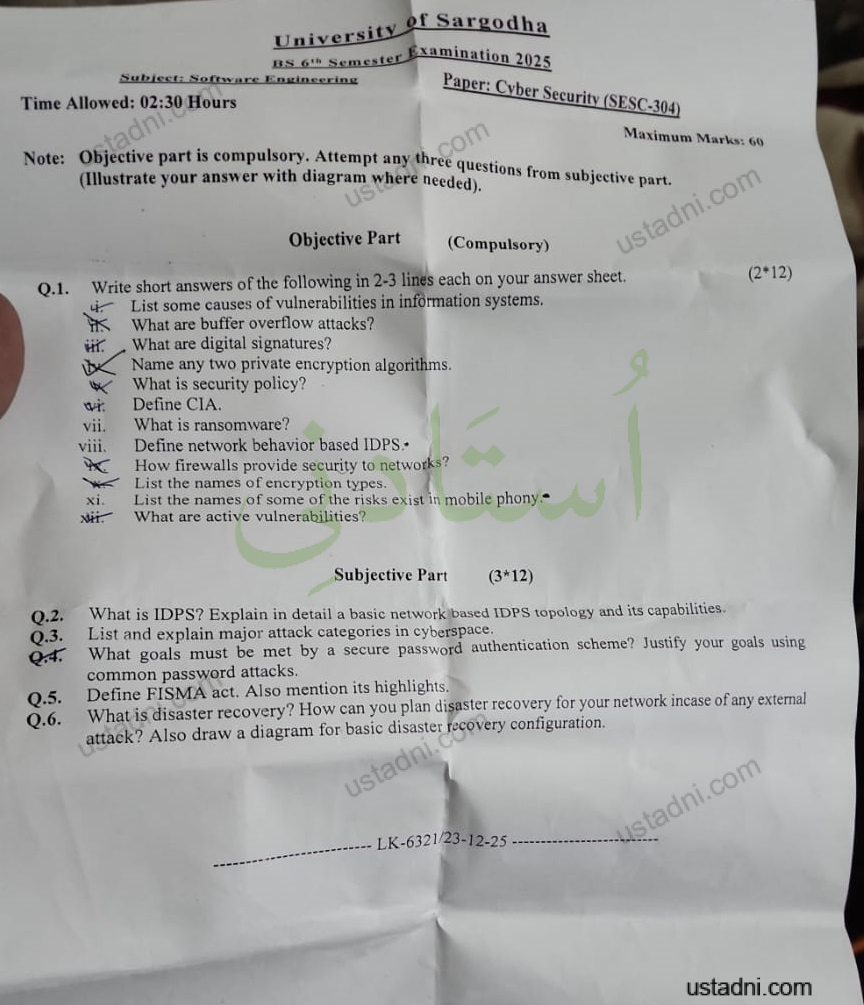
Cyber Security MS Software Engineering/PhD Software Engineering University Of Sargodha (UOS) 2025
Discussion
Ask a question about this paper, or help someone else with theirs. Answers are emailed to whoever asked.
No questions yet — be the first to ask.
More Cyber Security papers
See all Cyber Security BS/MS Cyber Security University Of Sargodha (UOS) 2026
Uploaded 8 months ago
Download ↓
 University of Sargodha ADP 1st Term Examination 2024 Subiect: I.T Paper: Introduction to ICT (ICTC-101) Time Allowed: 02:30 Hours
Uploaded 10 months ago
Download ↓
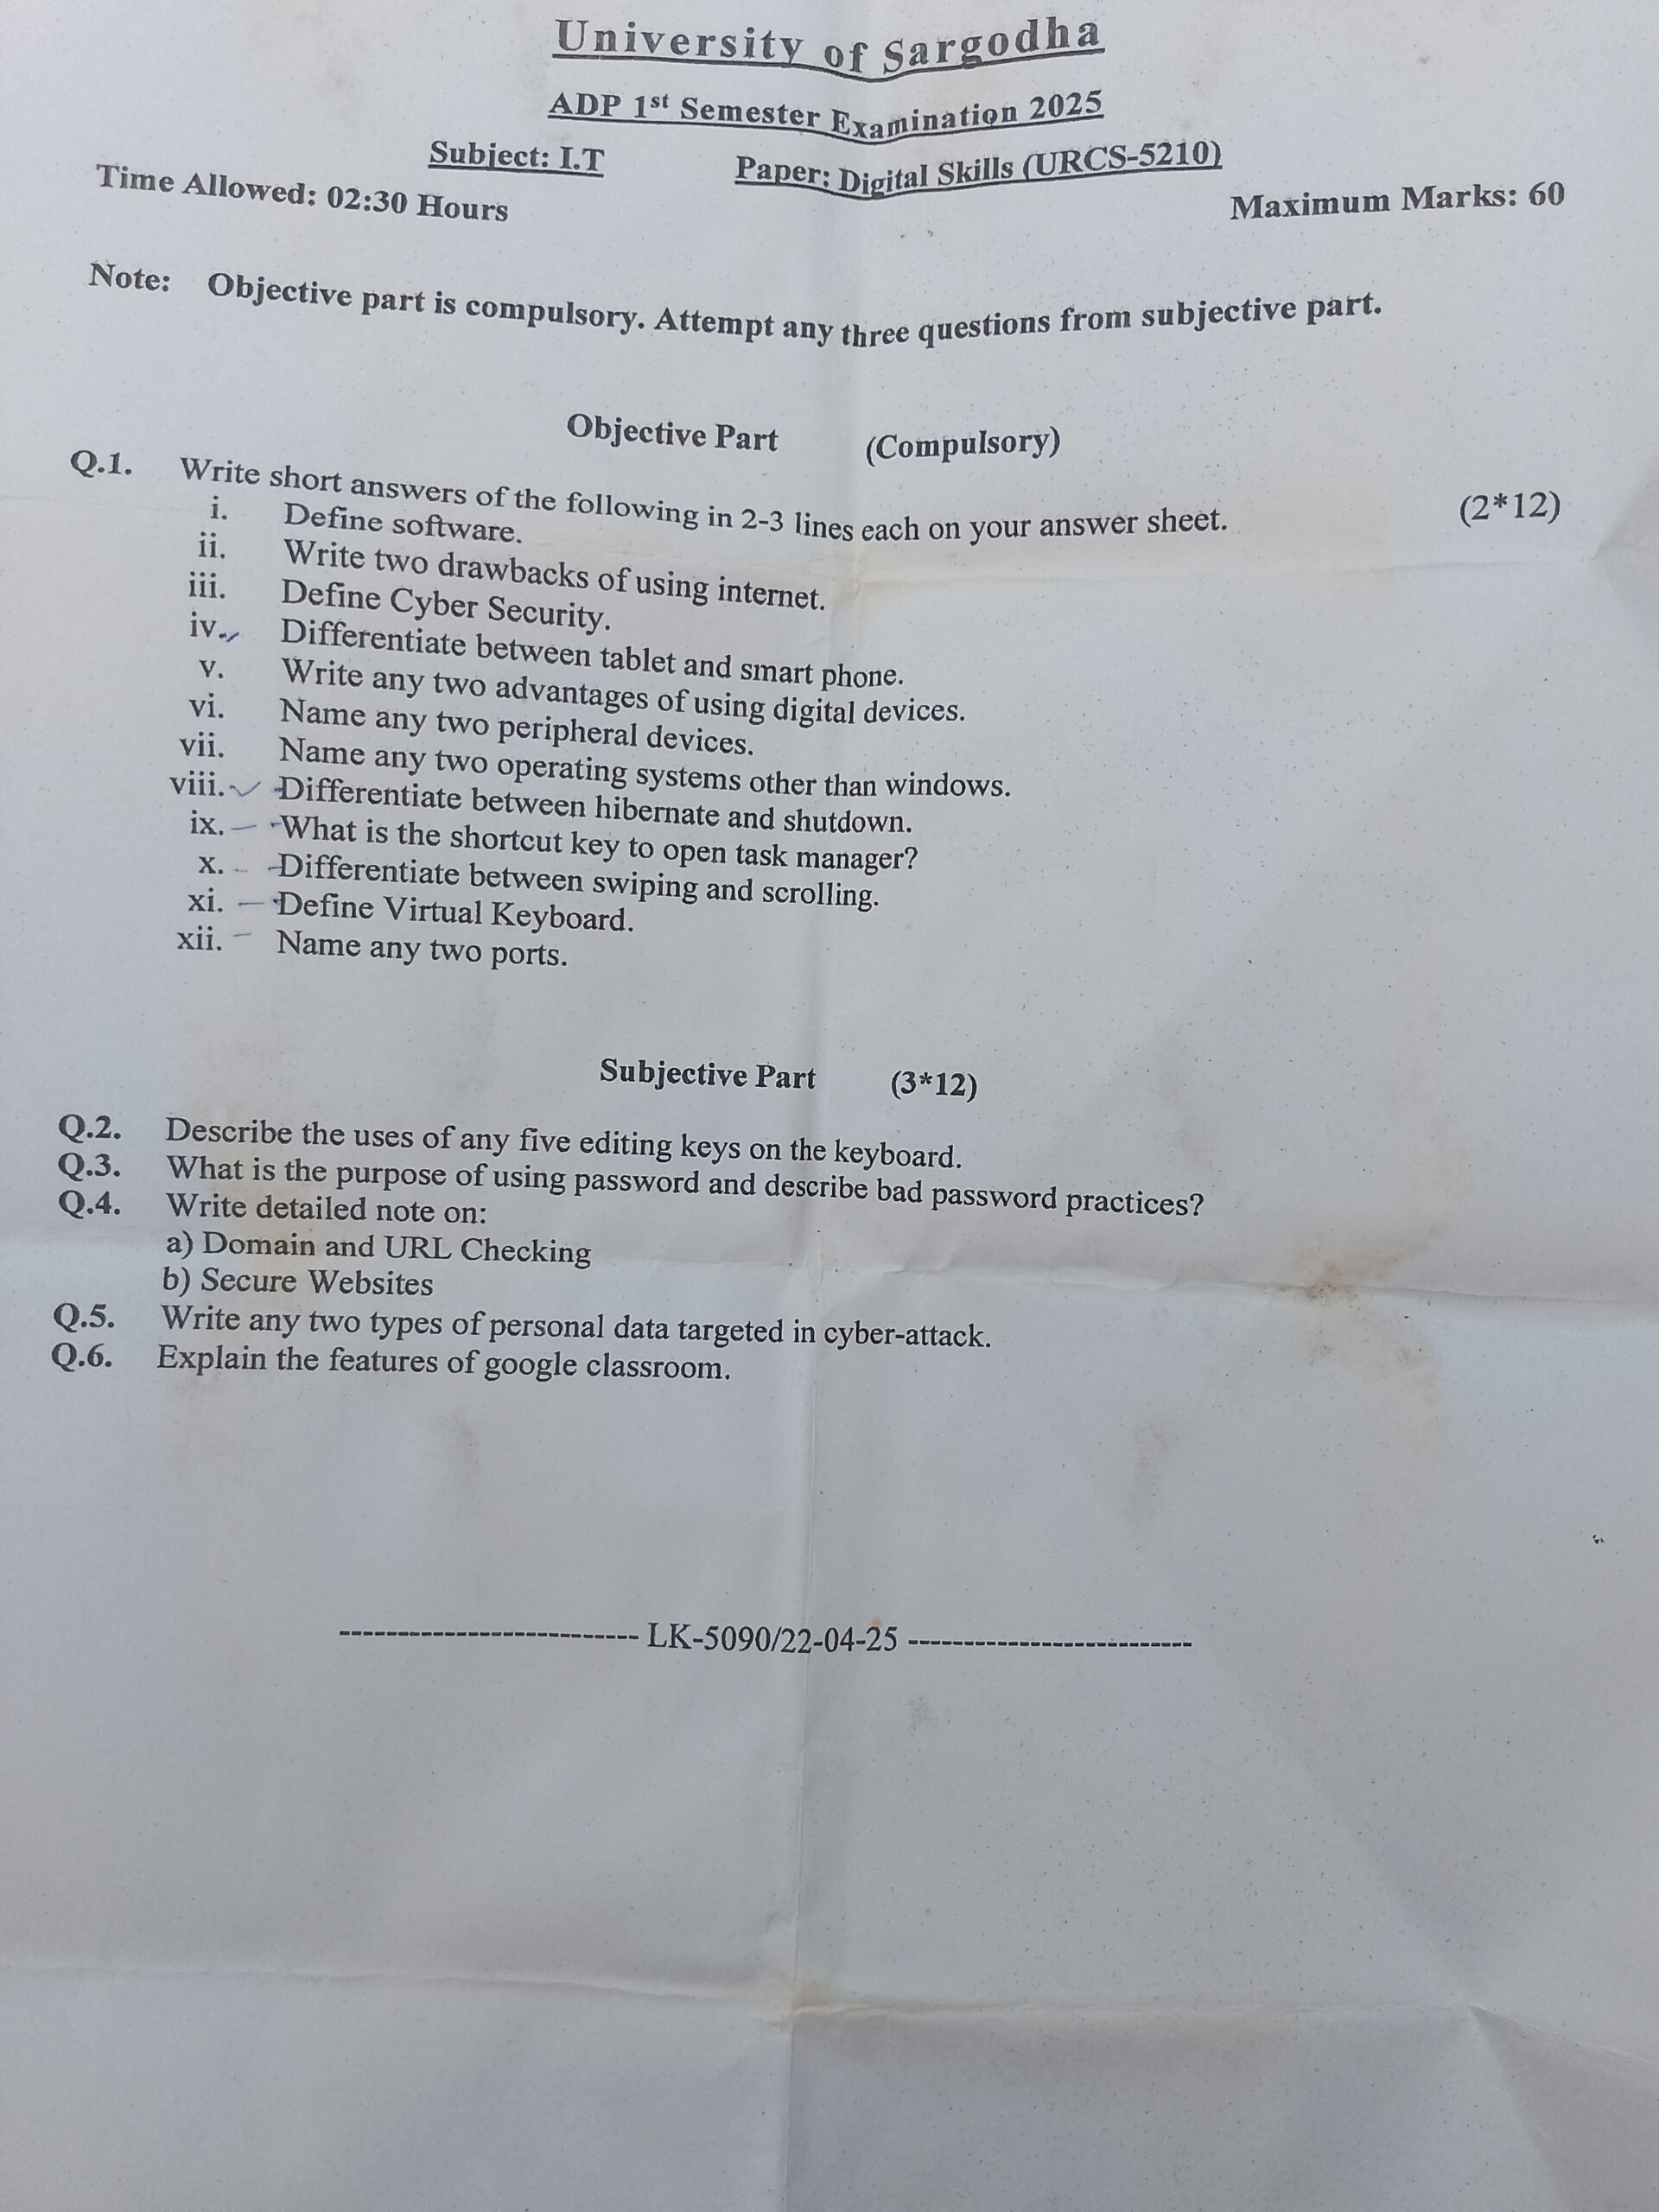 Cyber Security AD/ADP 1 Semester/Term University Of Sargodha (UOS) 2025
Uploaded 10 months ago
Download ↓
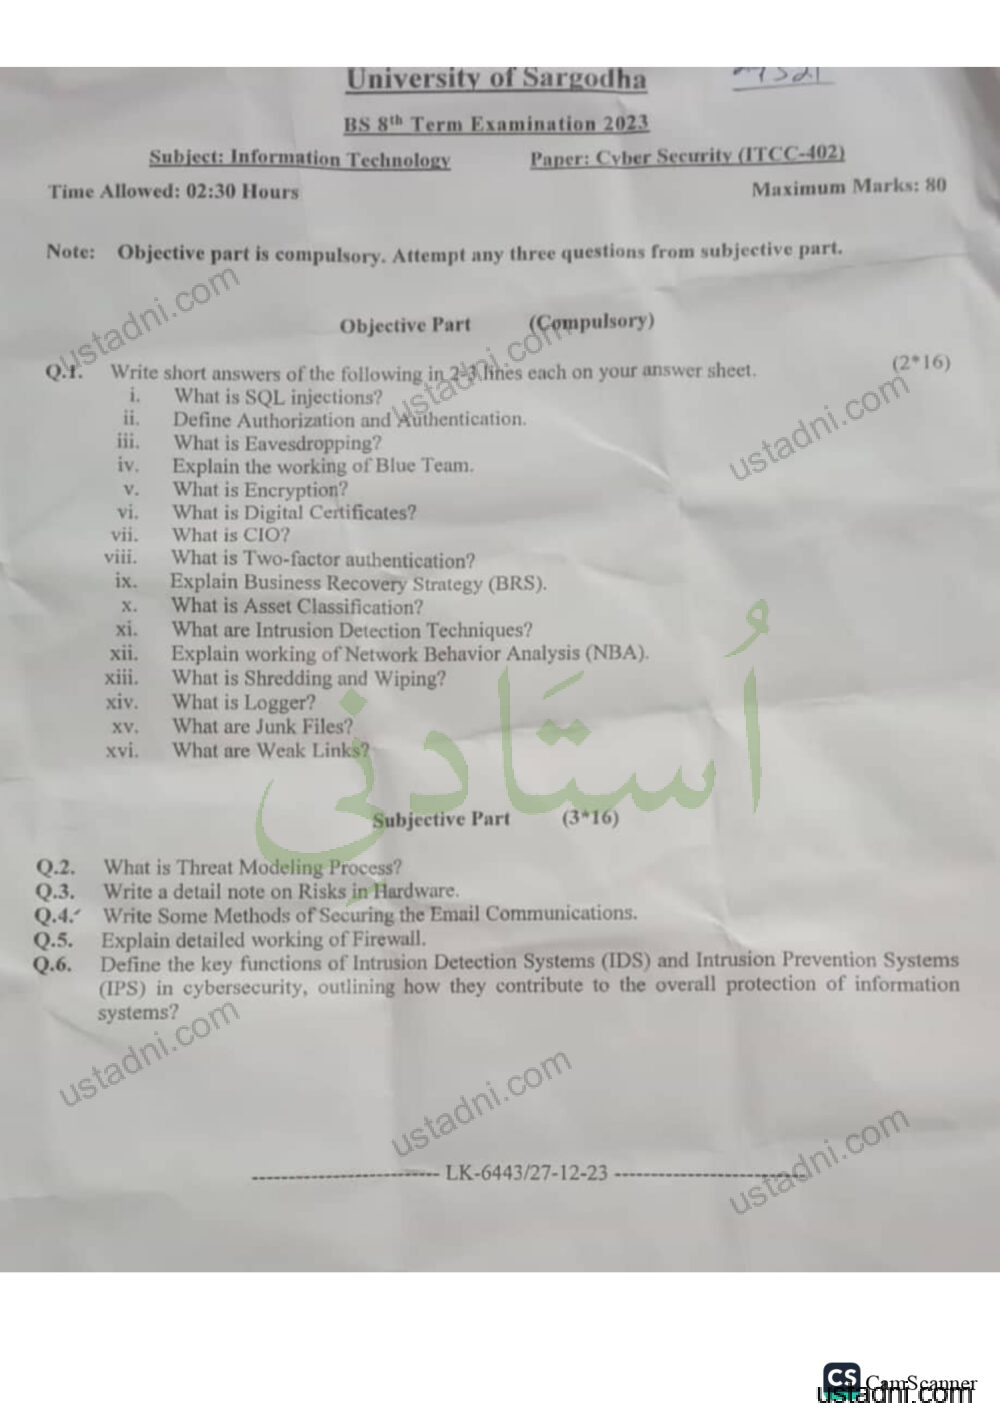 Cyber Security BS/MPhil Information Technology/MS Information Technology University Of Sargodha (UOS) 2023
Uploaded 1 year ago
Download ↓
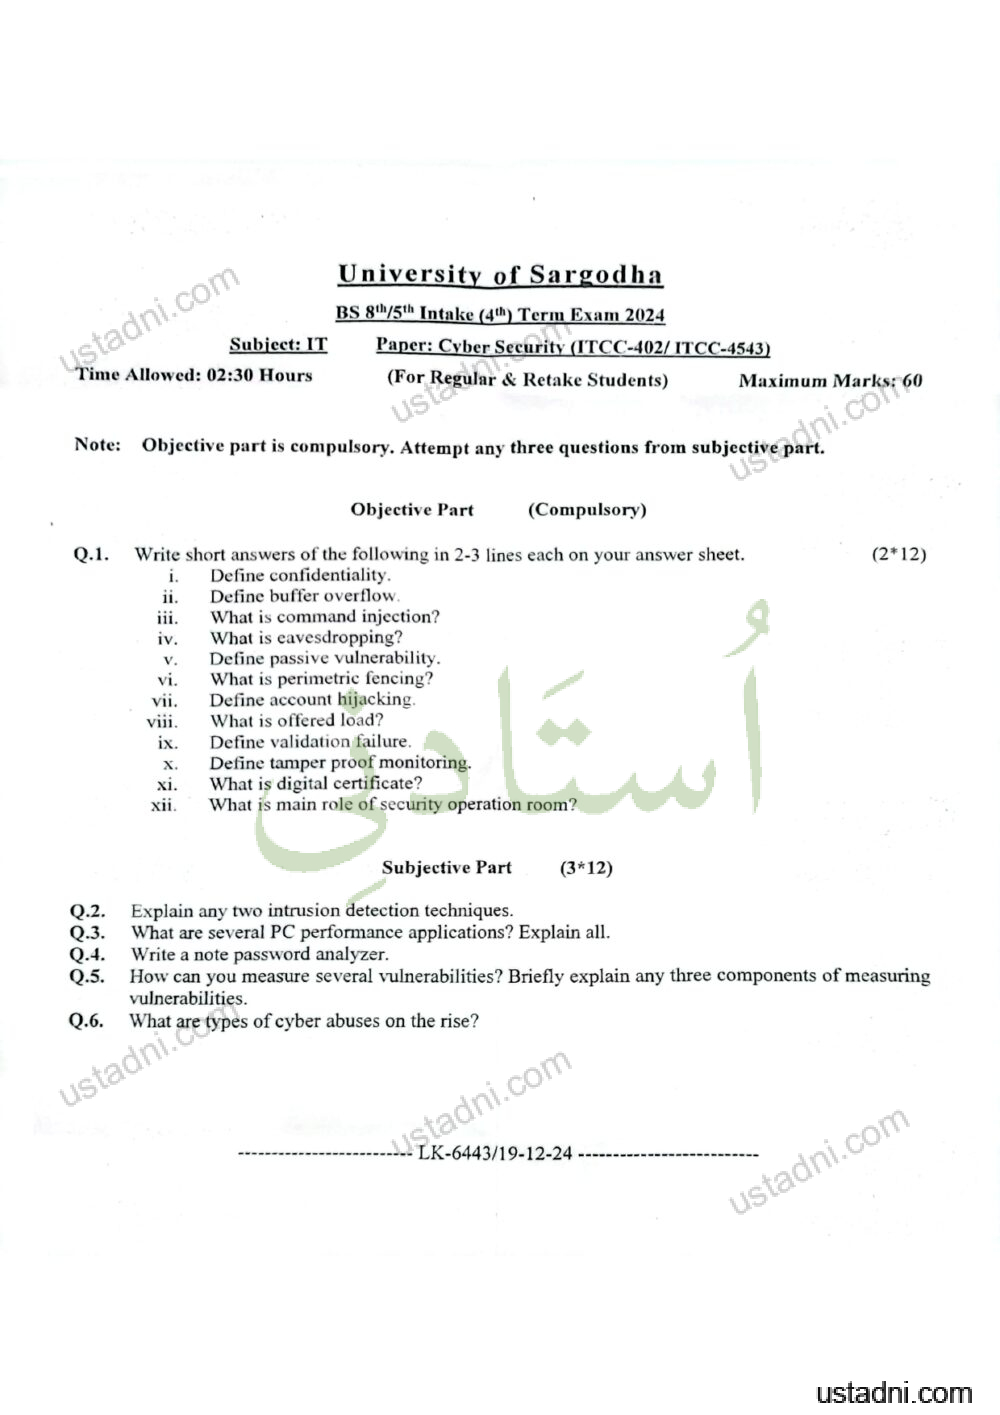 Cyber Security/Web Security BS 4 Semester/Term University Of Sargodha (UOS) 2024
Uploaded 1 year ago
Download ↓
Paper text
Inivers ;
ig PG: amination 2 25
Subject: Software Engineering Paper: C
: Cyber Seno:
Time Allowed: 02:30 Hours ber Security SESC-304
A Maximum Marks: 64
Note: Objective part is compulsory. Attempt any thre, quest;
(IMustrate your answer with diagram where Needed), 1008 from subjective part.
Q.1. Write short answers of the following in 2-3 lings each on your answer sheet. (2°12)
d— List some causes of vulnerabilities in information systems.
W< What are buffer overflow attacks?
wf. _ What are digital signatures?
wd Name any two private encryption algorithms.
Ww What is security policy?
ot. Define CIA.
vii. What is ransomware?
viii. Define network behavior based IDPS +
Time Allowed: 02:30 Hours
Maximum Marks: 64
Note: Objective part is compulsory. Attempt any three
: uest)
(Mlustrate your answer with diagram where ne Seep from subjective part,
Objective Part (Compulsory)
Q.1. Write short answers of the following in 2-3 ines each on your answer sheet. (2*12)
What are buffer overflow attacks?
wi. _. What are digital signatures?
vd Name any two private encryption algorithms.
vii. What is ransomware”?
viii. Define network behavior based IDPS »
1.
“W=" List the names of encryption types. |
List the names of some of the risks exist in mobile phony =
What are active vulnerabilities?
WC How firewalls provide security to networks?
X
Subjective Part (3*12)
Q.2. What is IDPS? Explain in detail a basic networkibased IDPS topology and its capabilities.
Q.3. List and explain major attack categories in cyberspace. y ” |
Q4. What goals must be met by a secure password authentication scheme? Justify your goals using
common password attacks. ~~
Q.5. Define FISMA act. Also mention its highlights, |
Q.6 What is disaster recovery? How can you plan disaster recovery lor your network incase of any external
il attack? Also draw a diagram for basic disaster fecovery configuration.
LK-6321/23<12-25 ---- see
-—
—————
SNL eae
-
ustadni.com